Hackers conducted reconnaissance before attacks on European refrigerators
Cybersecurity specialists have discovered that, several days before a series of attacks on refrigeration equipment in Europe, hackers extensively probed internet-connected cooling systems.
According to experts, this indicates a pre-planned and coordinated operation.
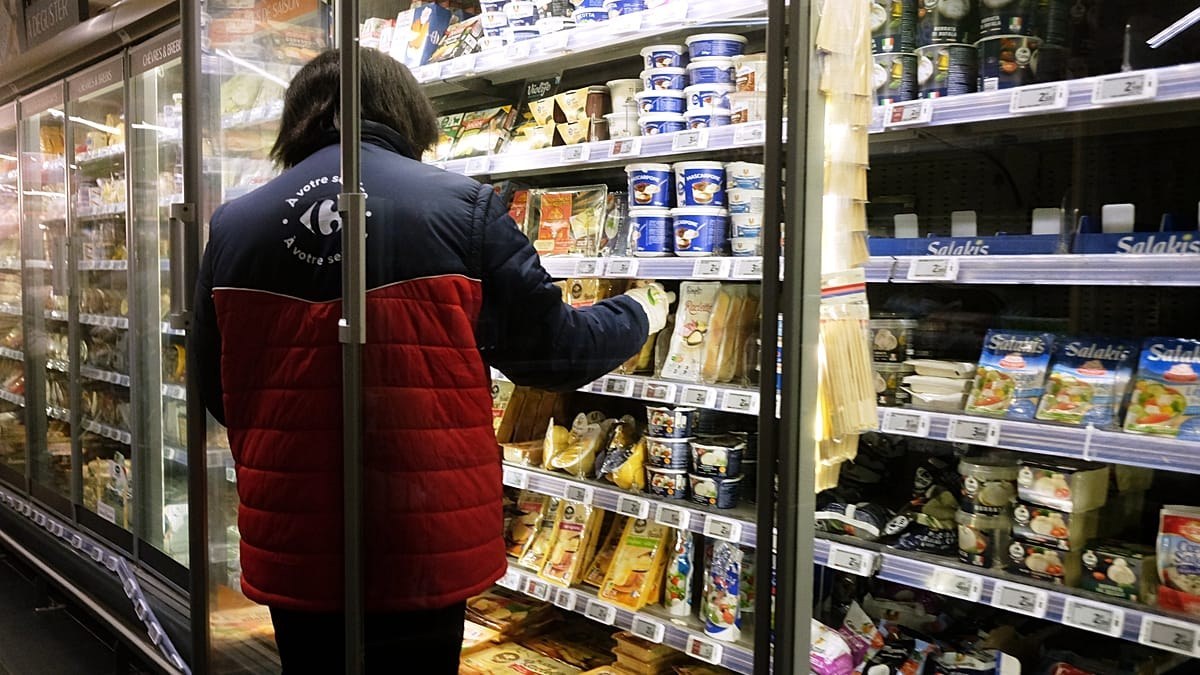
The attacks occurred on November 2 and 3. Targets included supermarkets in nine European countries, as well as several blood banks in France. Hackers exploited weak security and vulnerabilities in the AK-SM refrigeration system manager from Danfoss: they switched refrigerators and freezers to defrost mode and, in some cases, set temperatures as high as 50 degrees Celsius. Many stores had to dispose of spoiled products.
Experts warn that such vulnerabilities threaten not only retail. Refrigeration equipment in hospitals and data centers—infrastructure whose reliability is often taken for granted—could also be at risk.
Lupovis, a cybersecurity company, believes that a state actor may be behind the attacks. According to the company, between October 20 and 30, it recorded over 276 access attempts by 91 hackers targeting specific components of Danfoss controllers. The peak of activity occurred on October 26, and by the end of the month, it had subsided.